Password Hacking
We have passwords for emails, databases, computer systems, servers, bank accounts, and virtually everything that we want to protect. Passwords are in general the keys to get access into a system or an account.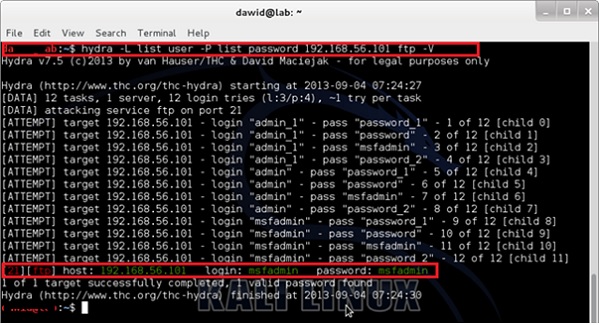
In general, people tend to set passwords that are easy to remember, such as their date of birth, names of family members, mobile numbers, etc. This is what makes the passwords weak and prone to easy hacking.
One should always take care to have a strong password to defend their accounts from potential hackers. A strong password has the following attributes −
- Contains at least 8 characters.
- A mix of letters, numbers, and special characters.
- A combination of small and capital letters.
Dictionary Attack
In a dictionary attack, the hacker uses a predefined list of words from a dictionary to try and guess the password. If the set password is weak, then a dictionary attack can decode it quite fast.
Hydra is a popular tool that is widely used for dictionary attacks. Take a look at the following screenshot and observe how we have used Hydra to find out the password of an FTP service.
Hybrid Dictionary Attack
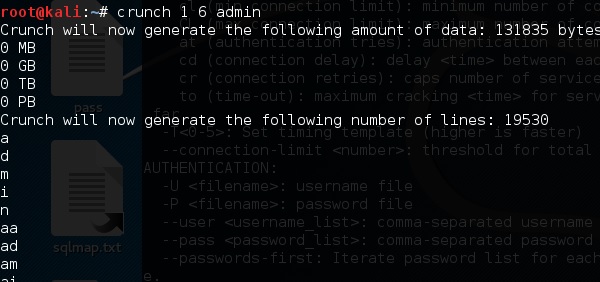
Hybrid dictionary attack uses a set of dictionary words combined with extensions. For example, we have the word “admin” and combine it with number extensions such as “admin123”, “admin147”, etc.
Crunch is a wordlist generator where you can specify a standard character set or a character set. Crunch can generate all possible combinations and permutations. This tool comes bundled with the Kali distribution of Linux.
Brute-Force Attack
In a brute-force attack, the hacker uses all possible combinations of letters, numbers, special characters, and small and capital letters to break the password. This type of attack has a high probability of success, but it requires an enormous amount of time to process all the combinations. A brute-force attack is slow and the hacker might require a system with high processing power to perform all those permutations and combinations faster.
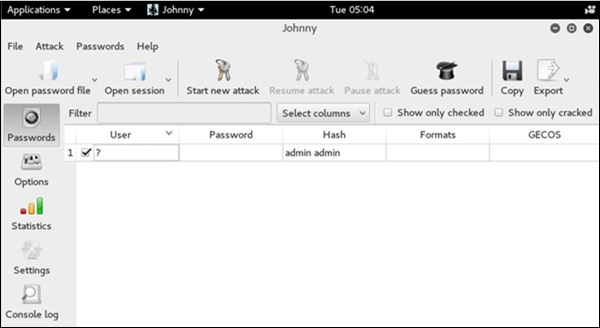
John the Ripper or Johnny is one of the powerful tools to set a brute-force attack and it comes bundled with the Kali distribution of Linux.
Rainbow Tables
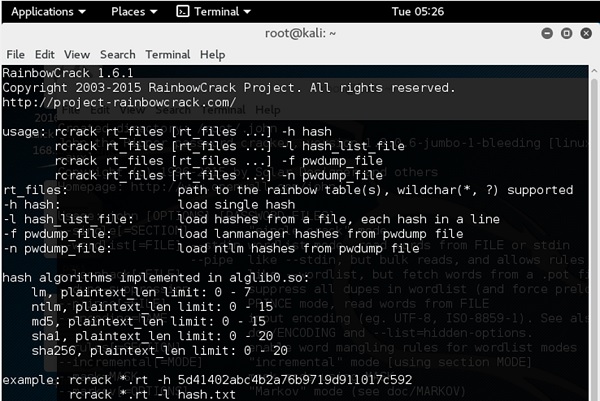
A rainbow table contains a set of predefined passwords that are hashed. It is a lookup table used especially in recovering plain passwords from a cipher text. During the process of password recovery, it just looks at the pre-calculated hash table to crack the password. The tables can be downloaded from http://project-rainbowcrack.com/table.htm
RainbowCrack 1.6.1 is the tool to use the rainbow tables. It is available again in Kali distribution.
Quick Tips
- Don’t note down the passwords anywhere, just memorize them.
- Set strong passwords that are difficult to crack.
- Use a combination of alphabets, digits, symbols, and capital and small letters.
- Don’t set passwords that are similar to their usernames.
Wireless Hacking
A wireless network is a set of two or more devices connected with each other via radio waves within a limited space range. The devices in a wireless network have the freedom to be in motion, but be in connection with the network and share data with other devices in the network. One of the most crucial point that they are so spread is that their installation cost is very cheap and fast than the wire networks.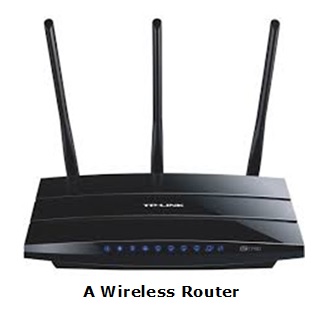
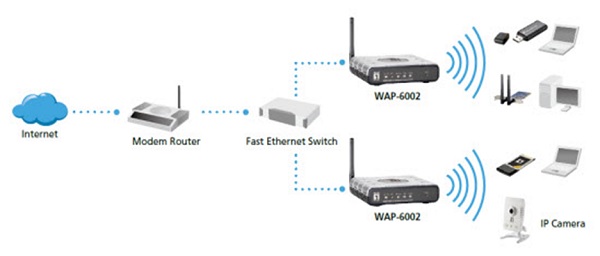
Wireless networks are widely used and it is quite easy to set them up. They use IEEE 802.11 standards. A wireless router is the most important device in a wireless network that connects the users with the Internet.
In a wireless network, we have Access Points which are extensions of wireless ranges that behave as logical switches.
Although wireless networks offer great flexibility, they have their security problems. A hacker can sniff the network packets without having to be in the same building where the network is located. As wireless networks communicate through radio waves, a hacker can easily sniff the network from a nearby location.
Most attackers use network sniffing to find the SSID and hack a wireless network. When our wireless cards are converted in sniffing modes, they are called monitor mode.
Kismet
Kismet is a powerful tool for wireless sniffing that is found in Kali distribution. It can also be downloaded from its official webpage − https://www.kismetwireless.net/index.shtml
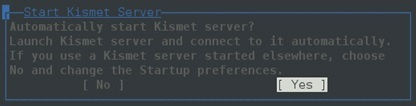
Let’s see how it works. First of all, open a terminal and type kismet. Start the Kismet Server and click Yes, as shown in the following screenshot.
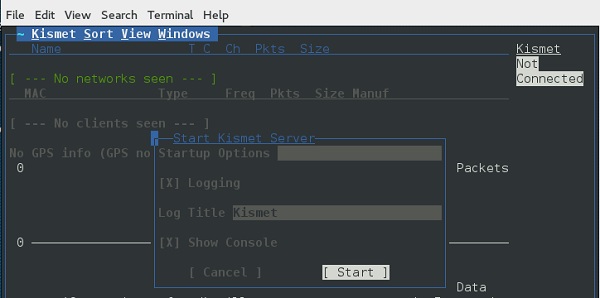
As shown here, click the Start button.
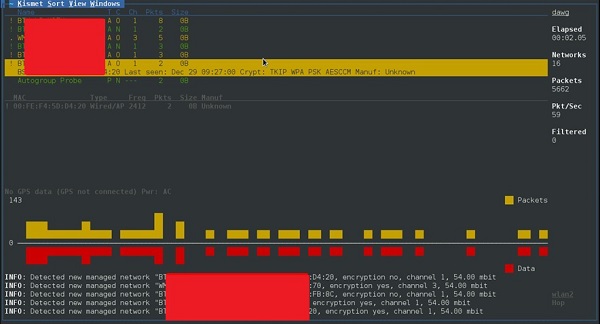
Now, Kismet will start to capture data. The following screenshot shows how it would appear −
NetStumbler
NetStumbler is another tool for wireless hacking that is primarily meant for Windows systems. It can be downloaded from http://www.stumbler.net/
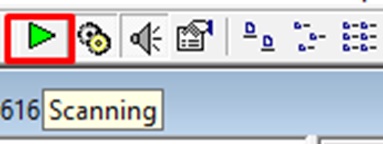
It is quite easy to use NetStumbler on your system. You just have to click the Scanning button and wait for the result, as shown in the following screenshot.
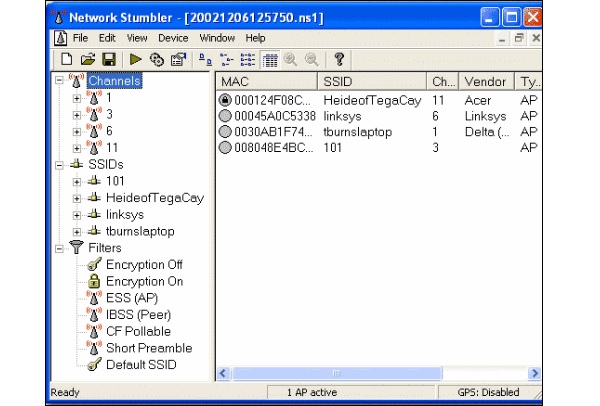
It should display a screenshot as follows −
It is important to note that your card should support monitoring mode, otherwise you will fail to monitor.
Wired Equivalent Privacy
Wired Equivalent Privacy (WEP) is a security protocol that was invented to secure wireless networks and keep them private. It utilizes encryption at the data link layer which forbids unauthorized access to the network.
The key is used to encrypt the packets before transmission begins. An integrity check mechanism checks that the packets are not altered after transmission.
Note that WEP is not entirely immune to security problems. It suffers from the following issues −
- CRC32 is not sufficient to ensure complete cryptographic integrity of a packet.
- It is vulnerable to dictionary attacks.
- WEP is vulnerable to Denial of Services attacks too.
WEPcrack
WEPcrack is a popular tool to crack WEP passwords. It can be downloaded from − https://sourceforge.net/projects/wepcrack/
Aircrack-ng
Aircrak-ng is another popular tool for cracking WEP passwords. It can be found in the Kali distribution of Linux.
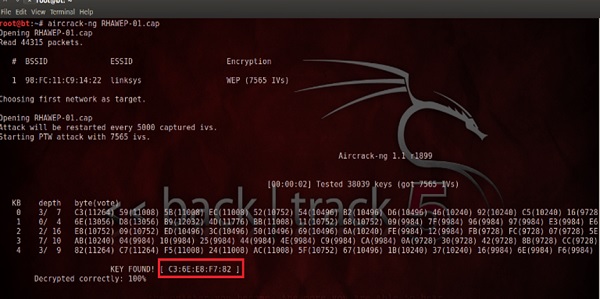
The following screenshot shows how we have sniffed a wireless network and collected packets and created a file RHAWEP-01.cap. Then we run it with aircrack-ng to decrypt the cypher.
Wireless DoS Attacks
In a wireless environment, an attacker can attack a network from a distance and therefore, it is sometimes difficult to collect evidences against the attacker.
The first type of DoS is Physical Attack. This type of attack is very basic and it is in the base of radio interferences which can be created even from cordless phones that operate in 2.4 GHz range.
Another type is Network DoS Attack. As the Wireless Access Point creates a shared medium, it offers the possibility to flood the traffic of this medium toward the AP which will make its processing more slow toward the clients that attempt to connect. Such attacks can be created just by a ping flood DoS attack.
Pyloris is a popular DoS tool that you can download from − https://sourceforge.net/projects/pyloris/
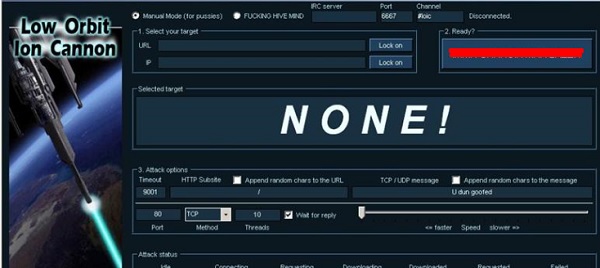
Low Orbit Ion Cannon (LOIC) is another popular tool for DoS attacks.
Quick Tips
To secure a wireless network, you should keep the following points in mind −
- Change the SSID and the network password regularly.
- Change the default password of access points.
- Don’t use WEP encryption.
- Turn off guest networking.
- Update the firmware of your wireless device.
Social Engineering
Let us try to understand the concept of Social Engineering attacks through some examples.
Example 1
You must have noticed old company documents being thrown into dustbins as garbage. These documents might contain sensitive information such as Names, Phone Numbers, Account Numbers, Social Security Numbers, Addresses, etc. Many companies still use carbon paper in their fax machines and once the roll is over, its carbon goes into dustbin which may have traces of sensitive data. Although it sounds improbable, but attackers can easily retrieve information from the company dumpsters by pilfering through the garbage.
Example 2
An attacker may befriend a company personnel and establish good relationship with him over a period of time. This relationship can be established online through social networks, chatting rooms, or offline at a coffee table, in a playground, or through any other means. The attacker takes the office personnel in confidence and finally digs out the required sensitive information without giving a clue.
Example 3
A social engineer may pretend to be an employee or a valid user or an VIP by faking an identification card or simply by convincing employees of his position in the company. Such an attacker can gain physical access to restricted areas, thus providing further opportunities for attacks.
Example 4
It happens in most of the cases that an attacker might be around you and can do shoulder surfing while you are typing sensitive information like user ID and password, account PIN, etc.
Phishing Attack
A phishing attack is a computer-based social engineering, where an attacker crafts an email that appears legitimate. Such emails have the same look and feel as those received from the original site, but they might contain links to fake websites. If you are not smart enough, then you will type your user ID and password and will try to login which will result in failure and by that time, the attacker will have your ID and password to attack your original account.
Quick Fix
- You should enforce a good security policy in your organization and conduct required trainings to make all the employees aware of the possible Social Engineering attacks and their consequences.
- Document shredding should be a mandatory activity in your company.
- Make double sure that any links that you receive in your email is coming from authentic sources and that they point to correct websites. Otherwise you might end up as a victim of Phishing.
- Be professional and never share your ID and password with anybody else in any case.


No comments:
Post a Comment